Hiring an external polygraph provider is like trying the mystery meat at a new restaurant. It could be a great choice or a big mistake. This is the main problem of outsourcing your truth-seeking.
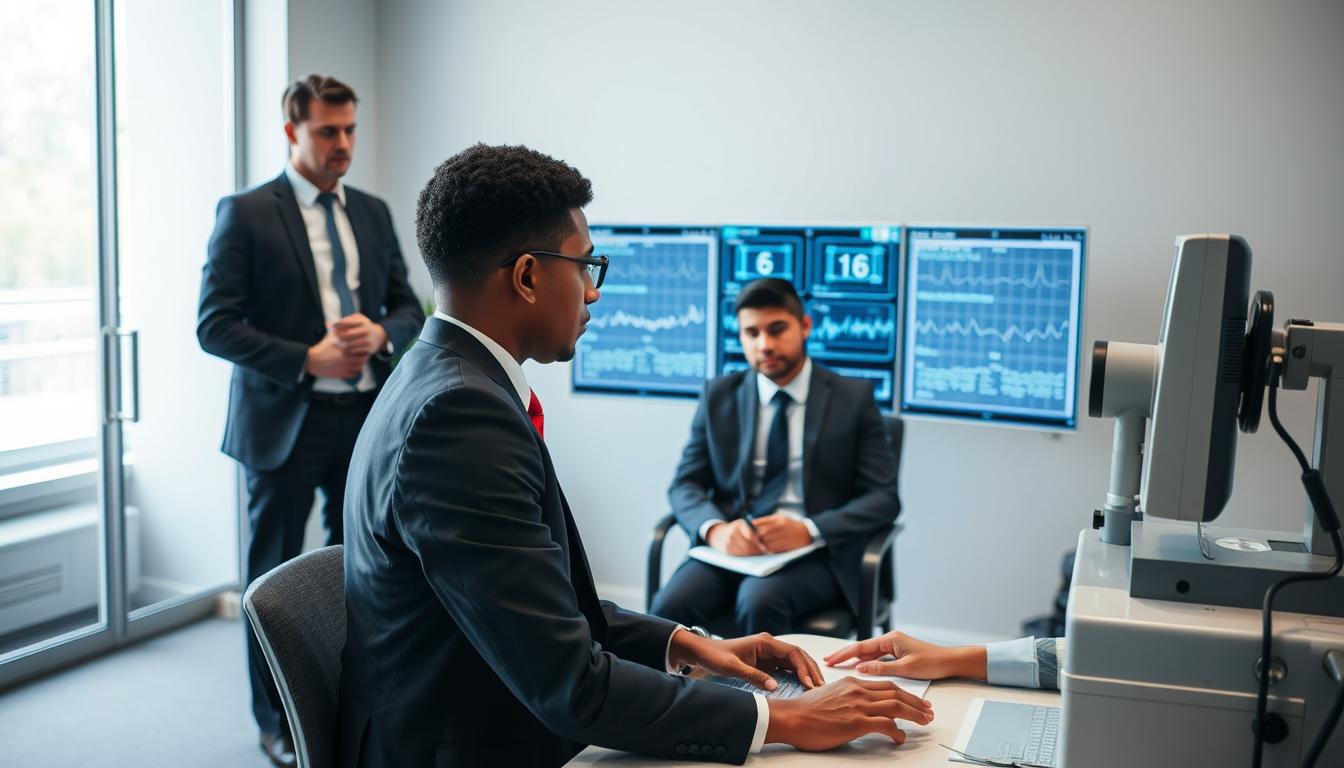
The good things are tempting. You get access to certified examiners with exciting backgrounds. They have the skills and tools to find the truth, like a spy thriller. They use advanced technology to check if someone is telling the truth.
But there’s a catch. You lose control over the process. This means the quality of service might vary. There’s also a risk of data privacy issues. It’s a trade-off: top-notch expertise versus keeping a close eye on everything.
So, how do you make a choice? We’ll look at both sides carefully. It begins with knowing the importance of checking things out, even if the vendor looks good.
Contracts and NDAs
In today’s world, vendor compliance is all about the details in a contract. It’s like a secret agent’s guide. This contract turns a vendor’s nice words into real, legal promises.
Why is this important? Vague promises don’t cut it anymore. A solid contract and NDA are like a blueprint for trust. They explain what’s confidential, where data can go, and what happens if it’s leaked.
Modern contracts must deal with global rules like GDPR. A good provider promises not to share your data with outsiders. But they might work with others. Your contract needs to list these companies.
For example, you might see “Film & Visual” for website work or “Mailchimp” for emails. This is okay; it’s about being open. The real vendor compliance magic is in where your data is kept. If it’s in Mailchimp’s US servers, the contract should say it’s safe under Privacy Shield.
Think of it as a detailed map of your data’s journey. This makes vendor compliance real. It turns a vague idea into something you can check. For more on these agreements, check out four key points of a modern contract.
These documents also set limits on what can be shared. Vendors can usually only talk if ordered by a court. This is your last line of defense. A strong contract doesn’t just promise safety; it makes it happen. It’s the quiet, but essential, part that lets the exciting analysis happen. Knowing this is key to seeing the value of an independent review.
Auditing Vendor Practices
Auditing a third-party polygraph provider is more than just checking boxes. It’s a deep dive into their operational integrity. You’ve chosen to outsource a critical function that relies on truth. Now, you must become a truth-seeker yourself.
This is where the rubber meets the road. Or, more accurately, where the polygraph chart meets the certified examiner’s trained eye.
Think of it as hiring a critic to review your own performance. The irony is delicious, but the stakes are high. Your vendor’s marketing might promise “unmatched expertise” and “rigorous protocols.” Your job is to turn those buzzwords into concrete evidence.
The Examiner’s Pedigree: Beyond the Cereal Box Diploma
First, the people. A vendor’s greatest asset is its examiners. The marketing material boasts “Highly Trained Examiners with law enforcement and military interrogation experience.” That sounds impressive, if true.
But how do you verify it? A certificate on the wall is a start, but it’s as meaningful as a celebrity’s autograph without provenance.
You need to ask for individual examiner credentials. Were they trained according to the highest international standards, as one source claims? Or was their training a weekend webinar? Request proof of continuous education. In the world of outsourcing veracity, an examiner’s skill fade is a real risk.
Look for a mix of backgrounds. A team with only former law enforcement might lack the nuance for corporate screening. A blend of experience is key. It’s the difference between a hammer looking for a nail and a sculptor looking for form.
Next, the tools. The polygraph instrument itself is a technological artifact. Is it modern, digital, and regularly calibrated? Or is it a relic from the Cold War era, about as reliable as a politician’s promise? Vendors often hide behind the phrase “state-of-the-art.” Your audit must define what that state actually is.
Ask about their software. Does it incorporate validated algorithms? How is data stored and secured? The “rigorous protocols ensuring reliability” mentioned in your source data must be documented. Can they show you a step-by-step process for a pre-employment test versus a specific incident investigation? If their answer is vague, consider it a red flag bigger than a matador’s cape.
Legal and Procedural Compliance: The Rulebook
Lastly, the framework. A outsourcing partner must operate within a “Legally Informed Process Aligning with best practices and jurisdictional standards.” This isn’t optional. Your liability doesn’t vanish when you delegate.
Audit their consent forms. Review their adherence to local laws regarding employee testing. Do their practices align with industry bodies like the American Polygraph Association? A thorough vendor audit should include a legal compliance checklist. It’s the shield that protects you when the questions get tough.
To help visualize this investigative process, here’s a breakdown of common vendor claims versus the concrete checkpoints you must verify.
| Vendor Marketing Claim | Your Audit Checkpoint | What to Ask For |
|---|---|---|
| “World-Class Certified Examiners” | Examiner Credential Verification | Individual certificates, training academy details, proof of ongoing education hours. |
| “Rigorous, Standardized Protocols” | Process Documentation Review | Written procedure manuals for different test types, evidence of protocol updates. |
| “Legally Compliant Operations” | Jurisdictional Compliance Check | Copies of legally-vetted consent forms, documentation of adherence to state/federal regulations. |
| “Cutting-Edge Technology” | Technology Stack Assessment | Make/model of polygraph instruments, software licensing agreements, data security policies. |
| “Unbiased, Accurate Results” | Quality Assurance Process | Blind review procedures, error rate statistics (if available), client feedback mechanisms. |
This table isn’t just a list; it’s your interrogation roadmap. Each checkpoint moves you from trusting a sales pitch to trusting a process. The goal of outsourcing this sensitive function is to gain expertise, not to inherit someone else’s problems.
In the end, auditing your vendor is an exercise in enlightened skepticism. You’re not being difficult; you’re being diligent. You’re paying for expertise, so you have every right to dissect it. When done right, this audit transforms your outsourcing decision from a leap of faith into a strategic partnership built on verified competence. After all, in the business of truth, there’s no room for convenient fictions.
Typical Service Reports
Think of the service report as the final product you paid for. It takes the squiggly lines and tells into a language you can use. This document is the key to understanding what was found.
A bad report feels like a dry manual. But a great one is like a story from a wise sage. It enlightens you, showing what’s important and what’s not. You want a report that gives you clear, actionable advice.
The best reports tell you what to do next. They help you make decisions, whether in court or a meeting. This is where vendor compliance really matters. The report proves their worth and justifies the cost.
It’s the document that helps you make your next move. Make sure your report does just that.