Pentagon Polygraph Testing in August 2026 gave employers, compliance officers, and security leaders a difficult case study: how far an organization should go when suspected leaks threaten sensitive information, and how to protect trust while doing so. The reported testing involved a national-security setting, not an ordinary workplace, but the integrity lessons are broader. Polygraph programs can support an inquiry only when their limits, scope, review process, and consequences are clearly defined.
The central workplace question is not whether an employer should ignore leaks. Sensitive information can affect safety, operations, and public accountability. The harder question is whether a testing campaign helps identify facts without damaging the trust that allows people to report concerns, cooperate with investigators, and follow confidentiality rules. That balance is where many integrity programs either gain credibility or lose it.
What Pentagon Polygraph Testing Showed
Pentagon Polygraph Testing Facts That Matter
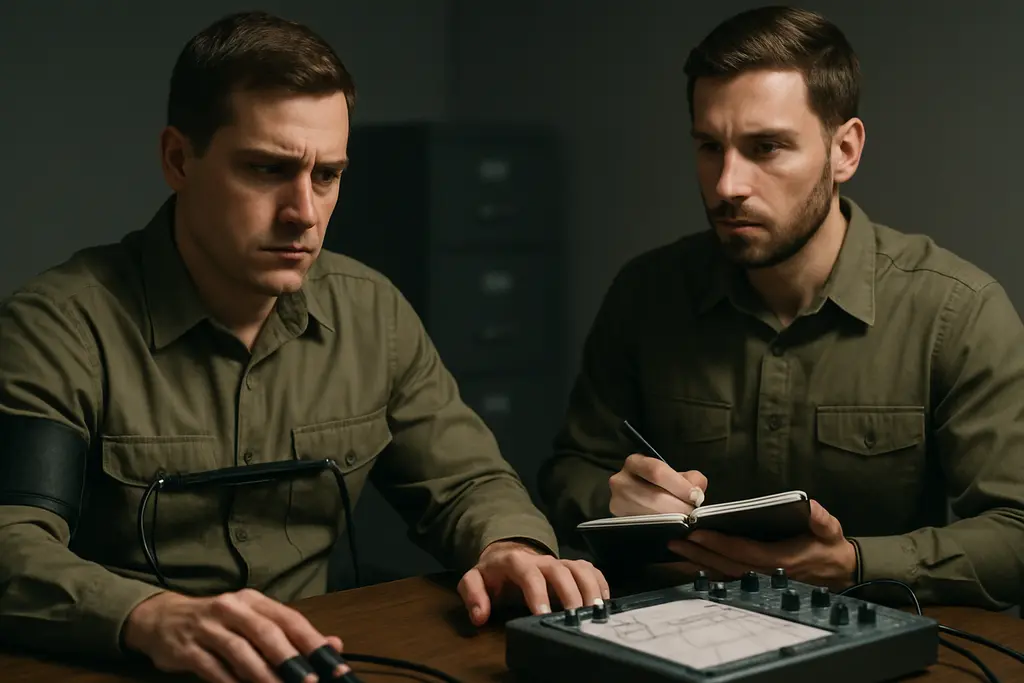
Reporting on the August 2026 leak inquiry said the Department of Defense subjected about 50 members of the Joint Staff, including military and civilian personnel, to polygraph tests after classified or internal information reached the media, including information about depleted munitions stocks during the U.S.–Iran war. The same reporting described the Joint Staff as roughly 1,500 to 2,000 officers and officials, meaning the sweep affected a limited but still significant share of that group, and characterized the scale and seniority of the testing as unprecedented in that context reported leak inquiry details.
Pentagon Polygraph Testing affected only part of the organization, yet it carried a wide signal. In any workplace, a highly visible integrity measure can be read in more than one way. Leaders may intend to show seriousness about confidentiality. Employees may read the same action as suspicion directed at a group rather than a focused investigation. Both reactions can exist at once, which is why process design matters.
Why Scale Changes Employee Perception
For employers, Pentagon Polygraph Testing is a reminder that scale changes the meaning of a control. A single examination tied to a specific evidentiary path is different from a wider sweep of people who share access, proximity, or rank. The broader the pool, the more important it becomes to explain selection criteria without disclosing investigative details that would compromise the inquiry.
Workplace integrity programs depend on more than enforcement. They rely on employees believing that rules are understandable, applied consistently, and reviewed through a fair process. If people believe testing is random, retaliatory, or disconnected from other evidence, the organization may gain short-term pressure but lose long-term cooperation. That risk is especially serious in sensitive environments where employees must report security failures, policy concerns, and operational mistakes.
Why Scope And Communication Matter
Define The Question Before The Examination
A polygraph examination is not a general audit of a person’s character. It is most defensible when the relevant issue is narrow, the examinee understands the process, and the result is evaluated with other information. A workplace program should therefore begin with a written purpose: what incident is under review, what information is being protected, who is within scope, and what other evidence will be considered.
That kind of structure does not remove uncertainty, but it reduces avoidable disputes. It also helps managers avoid treating a physiological response as a complete answer. A result may guide further inquiry, but it should not replace document review, access logs, witness interviews, forensic analysis, or policy assessment. For a related discussion of employee trust in this setting, see this analysis of Pentagon testing and employee trust.
Protect Reporting Channels
Leak investigations can unintentionally chill lawful or protected reporting if employees cannot distinguish between prohibited disclosure and proper internal escalation. The research record supplied for this article flags concerns that intensified internal surveillance may erode trust, that false positives may create unfair consequences, and that employees may become more hesitant to raise concerns. Those risks should be handled directly in policy language.
A practical integrity program should tell employees where concerns can be raised, which disclosures are prohibited, how confidentiality duties apply, and how the organization separates retaliation concerns from leak inquiries. That is not legal advice; it is a governance point. If employees have no trusted route for concerns, they may either stay silent or use unsafe channels. Neither outcome supports workplace integrity.
Polygraph Next And Technology Risk
Budget Requests Are Not Operational Proof
The research record also includes a technology development issue. In April 2026, the Defense Counterintelligence and Security Agency sought $6.421 million in fiscal year 2027 funding for a program called Polygraph Next, with a five-year plan totaling about $30.3 million for a next-generation system using AI, non-contact physiological sensors, and standoff sensing for credibility assessment reported budget request details.
A budget request is not the same thing as validated operational performance. For compliance leaders, that distinction is essential. Technology language can create an impression of precision, especially when AI and remote sensing are involved. Yet any credibility-assessment tool still requires validation, governance, human review, and clear rules about how outputs may be used.
Automation Can Magnify Weak Assumptions
The research notes identify concern that AI trained on polygraph-related data could carry forward unresolved reliability issues. Even without accepting or rejecting that concern as proven here, the compliance lesson is straightforward: automated scoring should not be treated as neutral simply because it is automated. If the input data, labels, or assumptions are disputed, the resulting system can reproduce those disputes at scale.
Organizations considering new screening or investigative tools should ask a short set of questions before adoption:
- What exact workplace problem is the tool meant to address?
- What evidence supports its use for that purpose and population?
- Who reviews the result before any employment or security consequence follows?
- How are errors, appeals, documentation, and access to records handled?
- How does the program protect lawful reporting and internal escalation?
These questions are not obstacles to integrity work. They are safeguards that help a program remain credible after the pressure of an incident has passed.
Building Integrity Without Overclaiming Results
Use Polygraph Results As One Input
Polygraph services are most useful when the organization is honest about what the examination can and cannot do. A polygraph records physiological activity associated with stress and response patterns during a structured examination. It does not read truth directly. In workplace settings, that means results should be weighed alongside independent evidence, not used as a substitute for it.
The same caution applies to communication with staff. Leaders should avoid promising certainty, instant answers, or guaranteed identification of a source. Better language is more restrained: the organization is investigating, multiple evidence streams are being reviewed, confidentiality obligations remain in effect, and employees will be treated through a defined process.
Trust Is A Compliance Asset
Trust is not soft or secondary. In sensitive workplaces, trust affects whether people report mistakes, preserve records, cooperate with interviews, and follow rules during pressure. A leak inquiry that damages internal trust may solve one problem while creating another. That is why controls should be paired with communication, training, access management, and consistent discipline standards.
Institutional memory also matters. Organizations that record why a control was used, what it found, what it failed to answer, and how policy changed afterward are less likely to repeat poor decisions. Readers interested in institutional records and related heritage topics can find material from the same network at Old Norse News.
Pentagon Polygraph Testing Integrity Lessons
Pentagon Polygraph Testing should be read as a cautionary workplace integrity case, not as a template for every organization. The August 2026 facts show a high-stakes leak inquiry involving a limited but notable portion of senior defense personnel. The Polygraph Next budget request shows interest in AI-assisted and sensor-based credibility assessment, but a request for funding does not answer questions about accuracy, fairness, or proper use.
The practical lesson is disciplined restraint. If a workplace uses polygraph examinations, it should define the purpose, limit the scope, document the evidence basis, protect reporting channels, and require human review before consequences follow. A serious integrity program does not need to overstate what polygraph testing can prove. It earns confidence by using every tool within clear limits, with enough transparency for employees to understand the process and enough caution to prevent one result from becoming an unsupported verdict.